
Open Data Structures: An Introduction
Computer ScienceTextbook
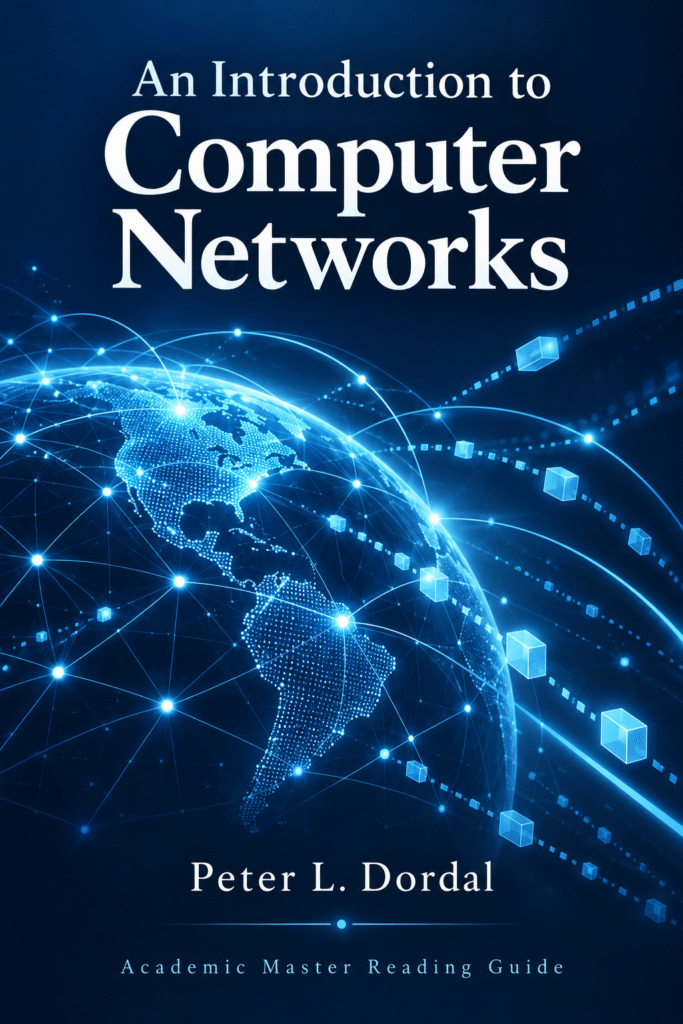
An Introduction to Computer Networks
Not rated yetRate this bookPeter L. Dordal’s An Introduction to Computer Networks connects network architecture with packet behavior, transport, performance, management, security, and simulation. The linked second-edition PDF is release 2.0.11, dated July 20, 2023. Thirty-two instructional chapters build from Ethernet and links through IP, routing, UDP, TCP, queuing, quality of service, SNMP, encryption, and practical learning environments. This guide follows that release. Its examples are models to reason with; implementation behavior, tools, and operational security guidance should be checked against current documentation before practical use.
Free reading is available at the official source. Opens in a new tab.
 Free
About this book
Peter L. Dordal’s An Introduction to Computer Networks connects network architecture with packet behavior, transport, performance, management, security, and simulation. The linked second-edition PDF is release 2.0.11, dated July 20, 2023. Thirty-two instructional chapters build from Ethernet and links through IP, routing, UDP, TCP, queuing, quality of service, SNMP, encryption, and practical learning environments. This guide follows that release. Its examples are models to reason with; implementation behavior, tools, and operational security guidance should be checked against current documentation before practical use.
Cover: original Academic Master reading-guide design. The linked textbook remains the source edition described above.
Book summary
About this book
Peter L. Dordal’s An Introduction to Computer Networks connects network architecture with packet behavior, transport, performance, management, security, and simulation. The linked second-edition PDF is release 2.0.11, dated July 20, 2023. Thirty-two instructional chapters build from Ethernet and links through IP, routing, UDP, TCP, queuing, quality of service, SNMP, encryption, and practical learning environments. This guide follows that release. Its examples are models to reason with; implementation behavior, tools, and operational security guidance should be checked against current documentation before practical use.
Chapter-by-chapter summaries
1. Overview of Networks
Layering separates responsibilities while allowing end-to-end communication. Distinguish a service offered by a layer from the protocol implementing it. Trace an application message through encapsulation and forwarding. The chapter establishes vocabulary for delay, addressing, links, and packets so later mechanisms can be related to the problem each solves.
2. Ethernet Basics
Local delivery involves frames, hardware addresses, and shared or switched access arrangements. Distinguish a destination’s local link identity from its IP identity. Trace how a frame reaches the next local recipient. The chapter explains foundational behavior rather than implying that historical shared-media Ethernet describes every modern switched installation.
3. Advanced Ethernet
Switching, learning, loops, and larger local-network arrangements introduce coordination beyond one simple segment. Follow the information a switch learns and the path a frame can take. Loops require particular attention because redundancy and repeated forwarding can interact badly. Compare topology with forwarding behavior rather than assuming a physical connection guarantees an appropriate path.
4. Wireless LANs
Wireless access faces shared-medium, interference, and mobility conditions different from a wire. Coordination and acknowledgment respond to uncertainty about reception. Identify what a sender can observe and what remains hidden. The chapter’s mechanisms should be understood as responses to those constraints rather than copied directly from a wired-network model.
5. Other LANs
Alternative local-network technologies illustrate different engineering choices. Compare access method, topology, addressing, and intended environment. A technology’s historical role can illuminate a design tradeoff without making it a current recommendation. The chapter broadens the reader’s model beyond assuming that one familiar LAN design is the only possible arrangement.
6. Links
A link’s capacity, delay, and transmission characteristics affect communication. Separate propagation from transmission time and both from waiting in a queue. Use units consistently in a short calculation. The chapter provides a physical and performance basis for understanding why increasing bandwidth does not remove every source of delay.
7. Packets
Packet organization, forwarding, and competing flows connect local mechanisms with a larger network. Identify which information belongs in a header and what decision uses it. Packet switching enables sharing but introduces queuing and loss. Trace a packet hop by hop rather than imagining a permanent dedicated path created for every message.
8. Abstract Sliding Windows
Windows allow multiple units to remain in flight while acknowledgments and sequence information coordinate progress. Distinguish window size, outstanding data, and retransmission. Trace a loss and acknowledgment sequence by hand. This abstract model prepares for transport protocols without requiring every later implementation detail at once.
9. IPv4
IP addressing and forwarding connect networks through a best-effort datagram service. Prefixes and routing entries determine next-hop decisions. Work a forwarding lookup with several overlapping prefixes. A destination address does not itself describe the full path. The chapter separates the packet’s destination from the router’s local decision about its next step.
10. IPv4 Companion Protocols
Supporting mechanisms address local resolution, configuration, and diagnostic or error information. Distinguish their roles instead of treating every control message as ordinary application data. Trace how a host obtains or uses information needed to send a packet. A diagnostic result provides evidence about a path or response, not a complete explanation of every failure.
11. IPv6
IPv6 changes addressing and protocol design while preserving the need for routing and local communication. Compare address representation, packet structure, and the source’s transition considerations with IPv4. More address space is important but not the whole design. Do not infer that a larger address alone makes a deployment correctly configured or secure.
12. Additional IPv6 Features
The chapter extends basic IPv6 with related mechanisms and operational questions. Identify which feature solves addressing, discovery, forwarding, or another problem. Trace the relevant messages in a small scenario. Keeping those functions separate makes comparisons with IPv4 more precise than assuming every familiar mechanism has an identical replacement.
13. Routing-Update Algorithms
Routers exchange information to build forwarding knowledge. Distance-vector and link-state approaches differ in what is shared and how routes are computed. Trace a topology change and the intermediate states. A final shortest-path result does not explain convergence behavior by itself. The chapter connects distributed information with the possibility of temporary inconsistency.
14. Large-Scale IP Routing
Aggregation and administrative organization make routing at scale different from one small graph. Distinguish an address plan, a forwarding table, and a routing policy. Analyse how a summary route reduces information and what assumptions make it appropriate. The chapter prepares for interdomain routing by showing that scale introduces organizational constraints as well as computational work.
15. Border Gateway Protocol
Interdomain routing incorporates policy and relationships rather than optimizing a single universal distance metric. Identify which autonomous systems advertise a route and why an operator might prefer one path. Separate reachability from willingness to carry traffic. The chapter explains why global routing cannot be understood as merely running a local shortest-path algorithm over the entire Internet.
16. UDP Transport
UDP supplies a transport-level datagram mechanism with ports and minimal additional services. Applications needing reliability or ordering must address those needs elsewhere. Distinguish delivery to a host from delivery to an application endpoint. A simpler transport can suit a task, but simplicity does not mean that loss, timing, or validation cease to matter.
17. TCP Basics
TCP organizes a reliable byte stream through connection state, sequence information, acknowledgments, and retransmission. A byte stream does not preserve the boundaries of application writes as separate messages. Trace connection activity and data progress. Distinguish receiver flow control from network congestion control, which answers a different question.
18. TCP Issues and Alternatives
Practical conditions expose limits and tradeoffs in transport design. Delays, losses, application patterns, and alternative approaches influence performance. Identify the specific problem before selecting an adjustment. The chapter encourages questioning assumptions behind a successful simple trace rather than assuming the same behavior under every network condition.
19. TCP Reno and Congestion Management
Congestion control adapts sending to signals about the network. Window changes reflect a control process rather than merely the amount an application wants to send. Trace the source’s phases and loss responses. Distinguish a congestion window from receiver-advertised capacity. This provides a baseline for understanding later implementations and performance examples.
20. Dynamics of TCP
Throughput and delay emerge from interactions among windows, round-trip time, loss, and competing traffic. Use a time-based trace rather than a static bandwidth figure. Explain why a nominally fast link can yield lower observed application throughput. The chapter connects protocol state with measurable behavior.
21. Further TCP Dynamics
Additional scenarios show how feedback timing, queues, and flow interactions complicate a simple model. Identify which assumptions changed from an earlier example. A formula is useful only within those assumptions. Compare a predicted steady state with transient behavior and explain why brief measurements may not represent a stable operating pattern.
22. Newer TCP Implementations
Later congestion-control designs make different choices about signals and adaptation. Compare their objectives and assumptions with the Reno baseline. A more recent algorithm is not automatically superior under every workload. The source’s implementations belong to its release date; current operating-system defaults and tuning should be checked separately.
23. Queuing and Scheduling
Buffers and service disciplines determine which packets wait, depart, or are dropped. Distinguish queue capacity from service rate. Compare scheduling choices using multiple flows and an explicit fairness objective. More buffering can reduce some losses while increasing delay, so evaluating a queue requires more than counting the packets it can hold.
24. Token Bucket Rate Limiting
Token-bucket models describe controlled average rates with permitted bursts. Separate token generation, bucket capacity, and packet arrival. Trace a short burst and a sustained stream. The mechanism’s behavior depends on parameters, and the same average rate can allow different short-term patterns. This prepares for quality-of-service policy.
25. Quality of Service
Service goals require classification, scheduling, policing, and coordination. Identify the promised metric and the mechanisms supporting it. Priority for one flow affects others, so the policy must be evaluated across the system. A label on traffic does not itself create a guaranteed end-to-end result.
26. Network Management and SNMP
Management uses observations to make decisions about faults, configuration, performance, and resources. SNMP provides information and operations but is not the whole management process. Distinguish a measured counter from the interpretation drawn from it. Identify what additional evidence is needed before treating a number as proof of a particular cause.
27. SNMP Versions 2 and 3
Protocol revisions change capabilities and security properties. Compare message handling and protection goals with the earlier baseline. Distinguish authentication and confidentiality rather than treating security as one switch. The source’s operational examples are educational; actual configuration should follow current supported practices and documentation.
28. Security
Threats and protections must be connected to assets, assumptions, and attacker capabilities. Separate confidentiality, integrity, authentication, and availability. Analyse what a proposed mechanism protects and what it leaves exposed. The chapter provides conceptual grounding, not a guarantee that deploying one technique makes a network secure.
29. Public-Key Encryption
Public-key techniques support different cryptographic functions through distinct protocols and trust arrangements. Distinguish encryption, signing, and key establishment. A correct mathematical operation does not automatically establish the identity associated with a key. Trace which party knows each value and what claim a successful check supports.
30. Mininet
An emulated environment enables controlled experiments with virtual network arrangements. Define the topology, traffic, and observation before running a test. Distinguish an emulation result from a universal production-network claim. Record commands, versions, and assumptions so another learner can reproduce the investigation in an authorized lab.
31. Simulation with ns-2
Simulation models selected network behavior under controlled assumptions. The chapter introduces building and interpreting experiments rather than treating a graph as self-explanatory evidence. State the model, variables, and measured outcome. Consider which real-world features are absent and whether their absence matters to the conclusion.
32. Simulation with ns-3
The final instructional chapter extends simulation-based study using another environment. Compare the experimental question and model choices before comparing numerical outputs. Reproducibility requires configuration and version details. The bibliography and selected solutions then support further reading and checking; they do not replace independent reasoning about why an experiment behaves as observed.
Study instructions
- Trace packets and protocol state with separate columns for layer, address, next hop, sequence state, and timing.
- Work delay and throughput problems with explicit units and assumptions.
- Compare routing algorithms by exchanged information, computation, policy, and convergence.
- Run emulation or simulation only in an authorized lab and preserve configuration and version notes.
- Use current official documentation before adapting implementation, security, or management examples operationally.
Questions for reflection
- Why does bandwidth not determine all delay?
- How does flow control differ from congestion control?
- Why does BGP include policy rather than one global metric?
- What does a simulation result fail to establish without its assumptions?
Sources and coverage
This original study guide covers all main chapters of the linked edition, or all instructional sections where the work has no numbered chapters. The explanations and suggested practice are written for study; consult the full source for cases, worked examples, illustrations, exercises, and references. Second edition, release 2.0.11, July 20, 2023. Operational details require current verification. Read the source edition.
About access & copyright
This page provides book information and study material. Full-text access is provided by the original publisher or authorised source; a listing does not grant permission to republish the book.
Read our Library Access & Copyright policyExplore the contents
Check the chapters covered in this edition.
Visit the official source
See reading, preview or purchase options.
Save for later
Keep this textbook in your saved collection.
Reader ratings & reviews
Share your thoughts
Your review helps other students choose the right resources.
KEEP LEARNING
Your next great read
Computer Science
Foundations of Computation
Foundations of Computation
View Foundations of Computation — bookThink Bayes: Bayesian Statistics Made Simple
Think Bayes: Bayesian Statistics Made Simple
View Think Bayes: Bayesian Statistics Made Simple — book Computer Science
Python for Everybody: Exploring Data Using Python 3
View Python for Everybody: Exploring Data Using Python 3 — book Computer Science
Introduction to Computer Graphics
View Introduction to Computer Graphics — book Computer Science
Introduction to Programming Using Java
View Introduction to Programming Using Java — book Computer Science
Nature of Geographic Information
View Nature of Geographic Information — book Computer Science
Java with BlueJ Part 2
View Java with BlueJ Part 2 — book Computer Science
Java with BlueJ
View Java with BlueJ — book Computer Science



